Block Malicious Packages
Before They Install
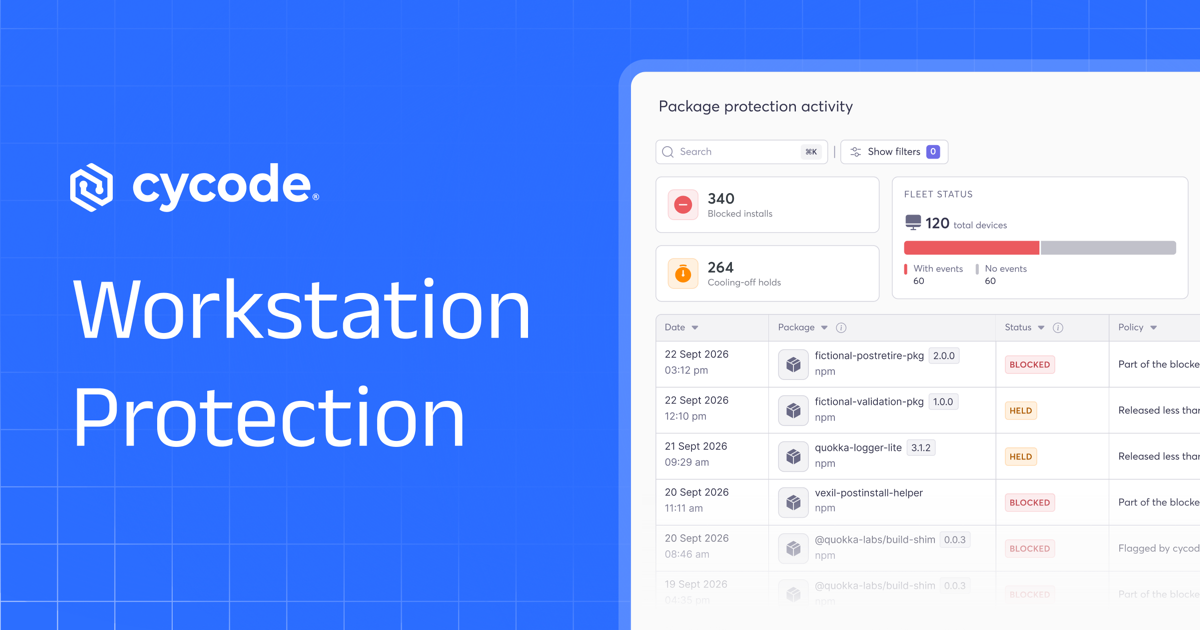
Stop software supply chain attacks before they start. Cycode Workstation Protection blocks malicious packages before developers or agents install them.


Extend Agentic Development Security to Developer Workstation
Software supply chain attacks have moved upstream, weaponizing trusted open-source packages that developers and agents install before traditional security checks run. Protect every workstation from supply chain attacks in real time.
Block Malicious Packages
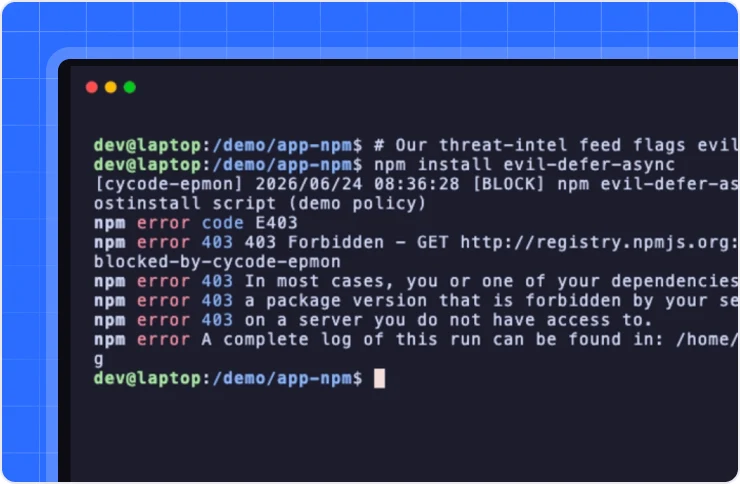
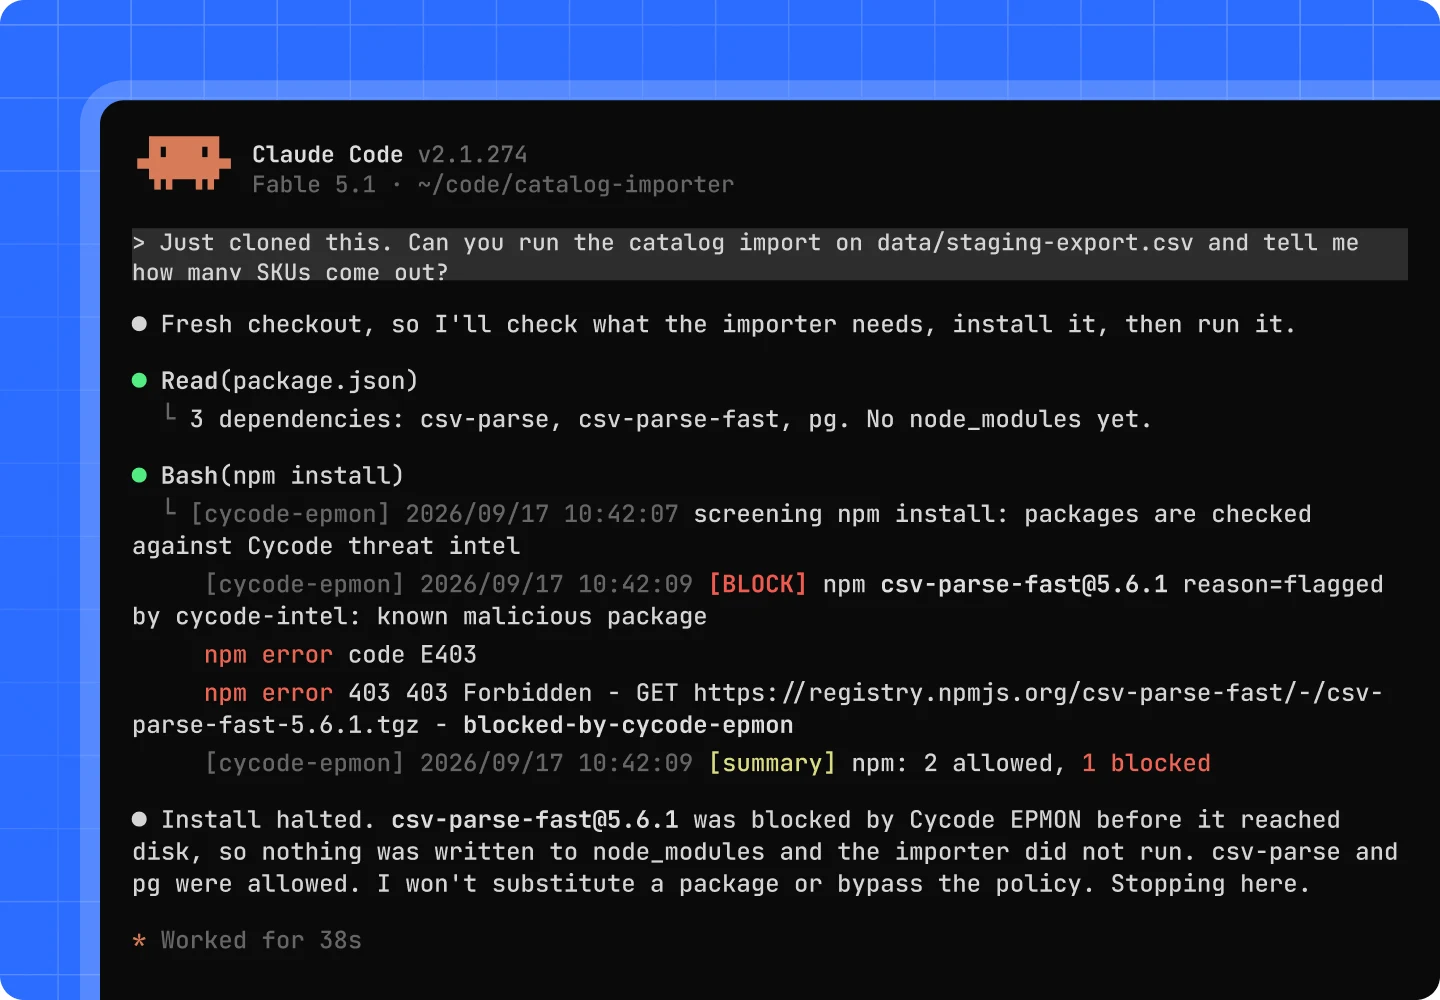
Check every package against a live threat intelligence feedEvery install is checked against a continuously updated threat intelligence feed. Confirmed-malicious packages are stopped regardless of when they were published, including versions that have already aged past a cooldown window.
Enforce Cooldown Policies
Protect against malicious versionsof trusted packages
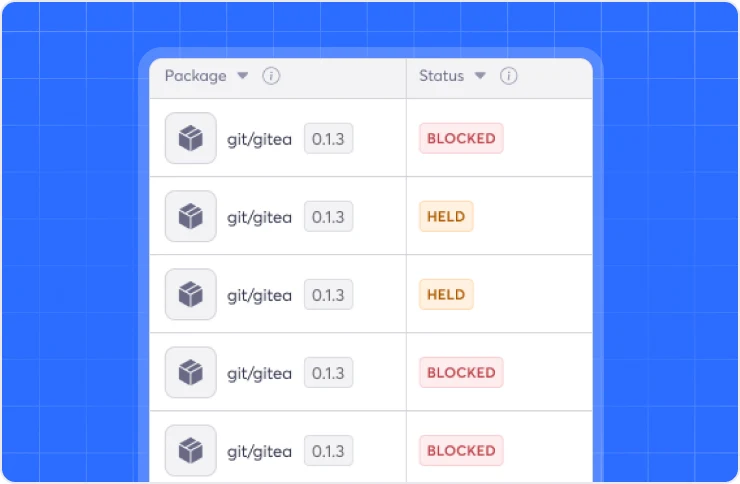
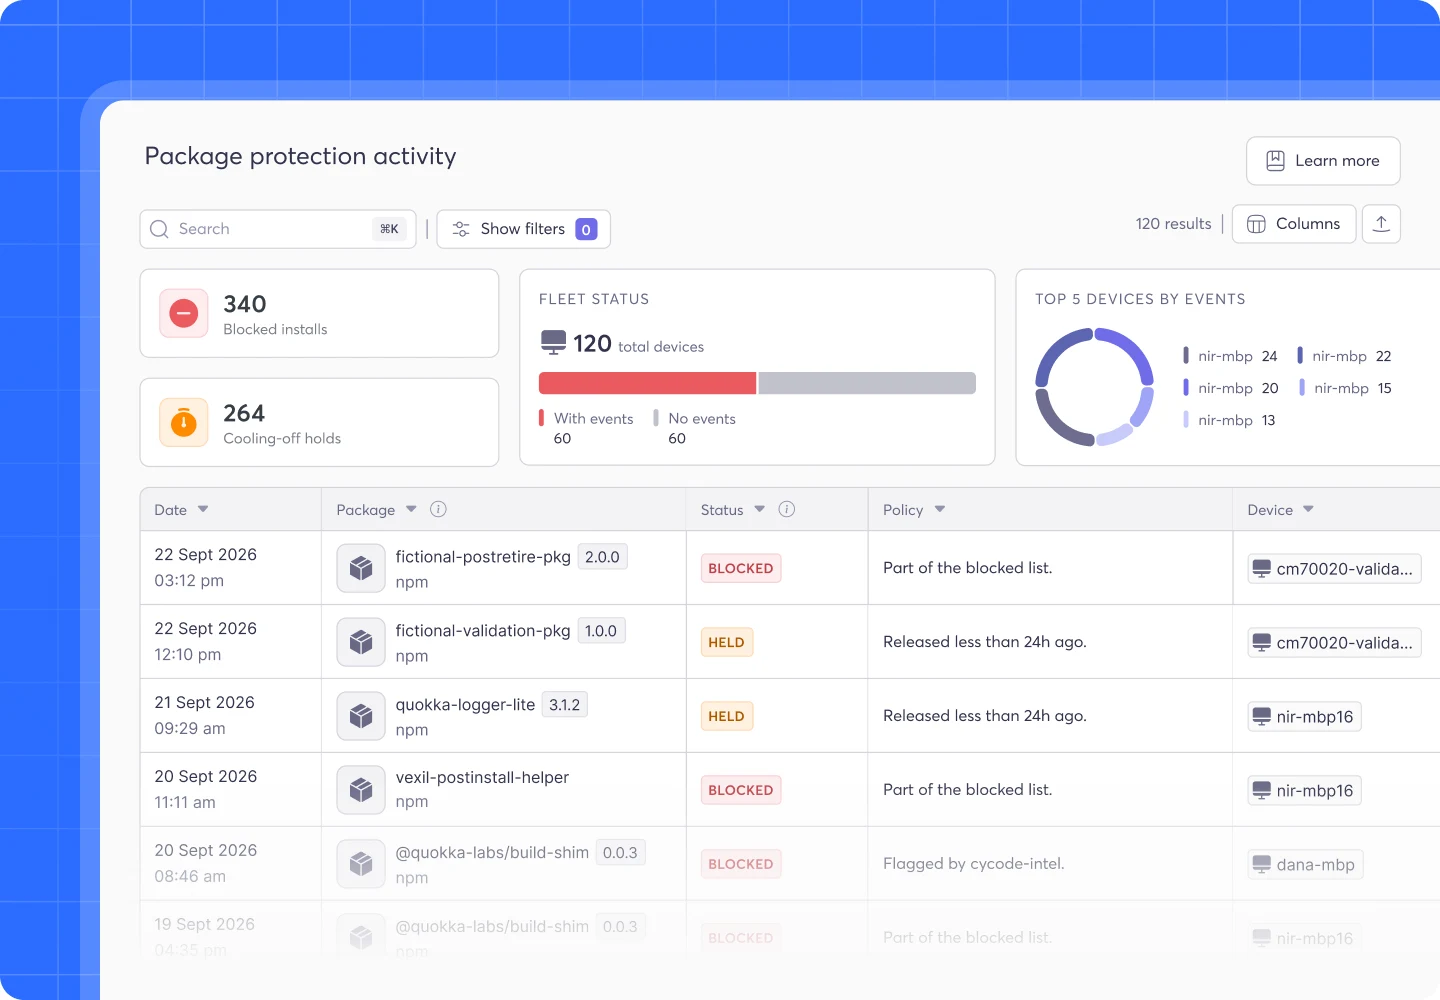
Release-age gating blocks versions published too recently to have been scrutinized, the window in which compromised releases are most often installed. Enforcement happens on the device, so the policy holds no matter what a developer or agent is running.
Protect every workstation
Deploy across the expandingattack surface
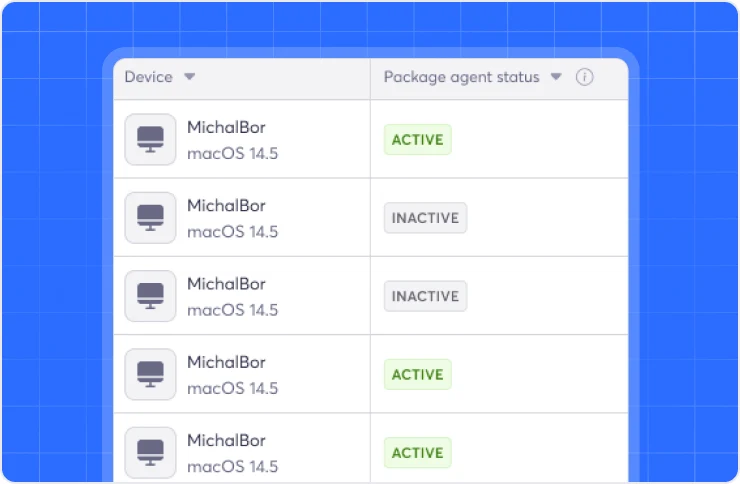
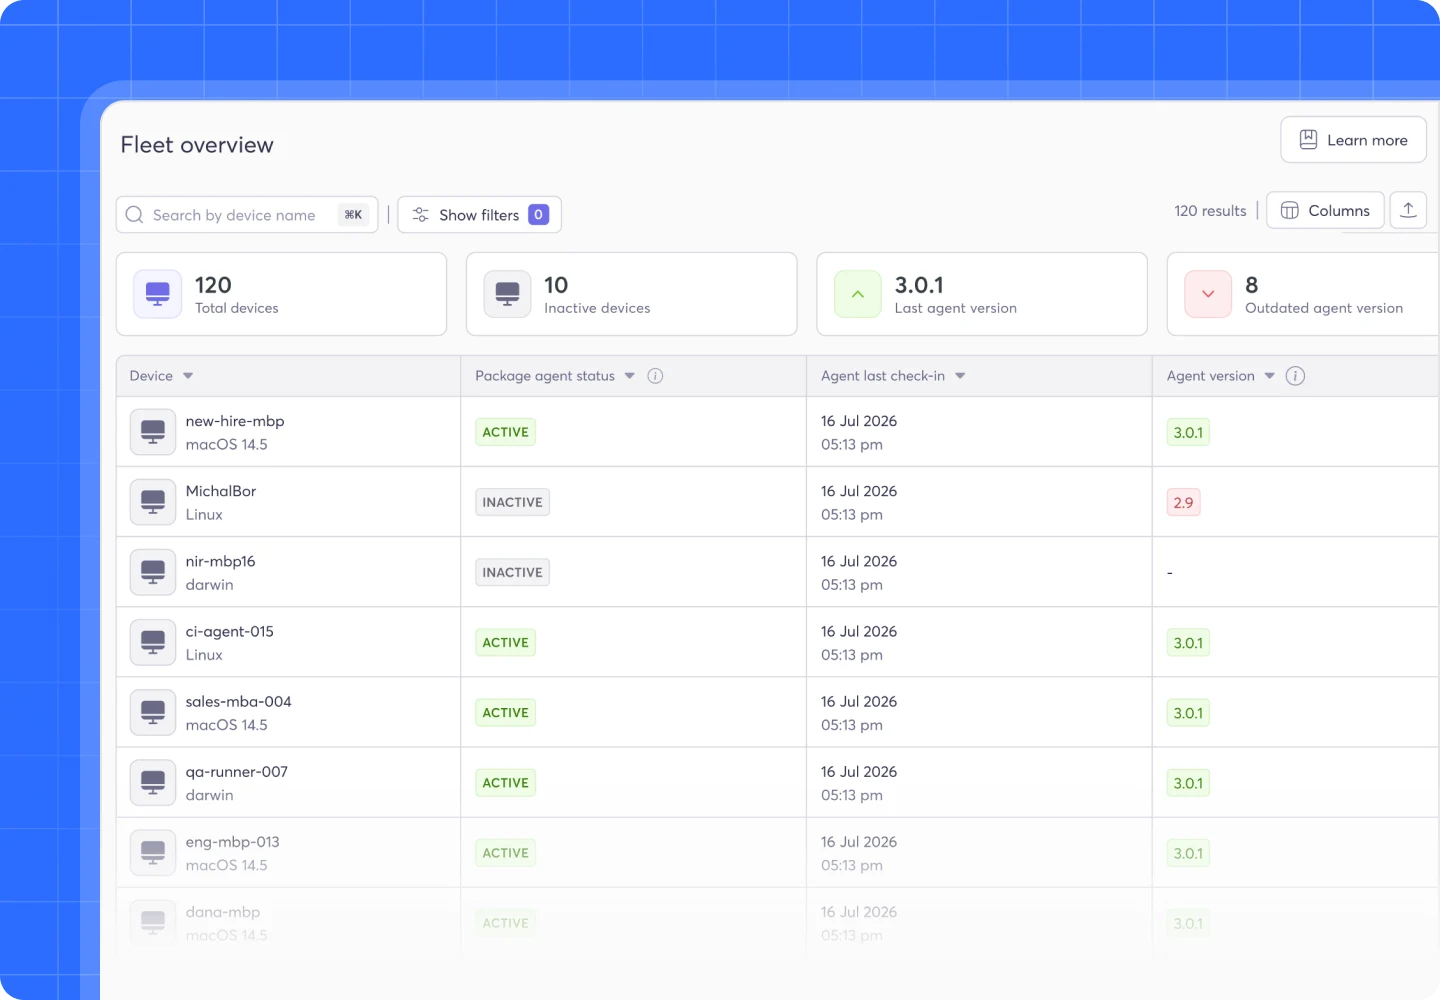
AI development has expanded the attack surface from a few devices to every workstation with a coding agent. Protect them all with one lightweight control that deploys at speed and scale through MDM and covers every developer workstation.
Stop software supply chain attacks Before they start
Supply chain defenses that start downstream of the device are often too late. A credential-rich machine is exposed before code is generated or a security check runs on a pull request. Cycode makes the install command an enforcement point, evaluating every package before it reaches the machine.
Leverage the ecosystem to Catch compromised packages
Software supply chain attacks often hijack trusted packages to ship a malicious version. Cooldown policies block recently published versions, giving maintainers and researchers time to find and flag malicious versions.
Protect Every Workstation from malicious packages
Coding agents expanded the attack surface to every workstation with source repositories, cloud credentials, SSH keys, publish rights, and coding agents that can read and traverse the codebase. Cover them all.
Unify code risk into one Agentic Development Security Platform
One platform, one graph, one agentic engine. Cycode unifies control, context, and autonomy in a single architecture that integrates into the tools your developers, security teams, and AI agents already use.

Explore Our Resources
5 AI Security Maturity Models Compared (2026)
Read More
Agentic Development Lifecycle (ADLC): What You Need to Know
Read More
Agentic SCA: Triage, Mitigate, and Fix Exploitable CVEs Without Breaking Changes
Read More
Intellectual Property Leakage: Risks, Detection, and Prevention
Read More
Introducing Agentic Workflows: Put Agents to Work for Security
Read More
Introducing Bulk AI Exploitability Analysis: Prioritize Exploitable Vulnerabilities at Scale
Read More
What Is DAST? Dynamic Application Security Testing in the Agentic Era
Read More
The Role of Agentic AI in Cyber Security
Read More
SBOM Automation: Tools and Guide
Read More
AI Code Security: Complete Guide
Read More
6 Steps to be Mythos Ready: How to Prepare for the AI Vulnerability Storm
Read More
What Is an AI Vulnerability Scanner?
Read More
Introducing Cycode Maestro: The Security Conductor of Your Agentic SDLC
Read More
Shedding The Lite: Unfolding The Dramatic Turn of Events with the LiteLLM Compromise
Read More
Agentic Appsec Has Arrived
Read More
Introducing AI Security: A Dedicated Violation Category for AI Risk in Application Security
Read More