
Cycode: The Modern Veracode Alternative For Application Security
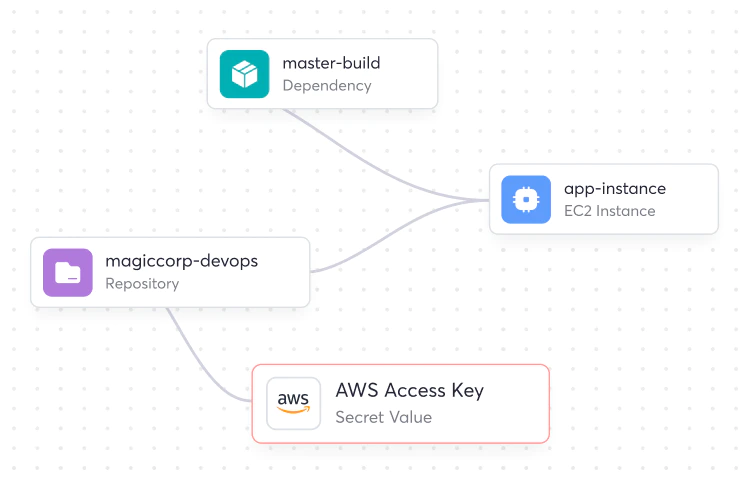
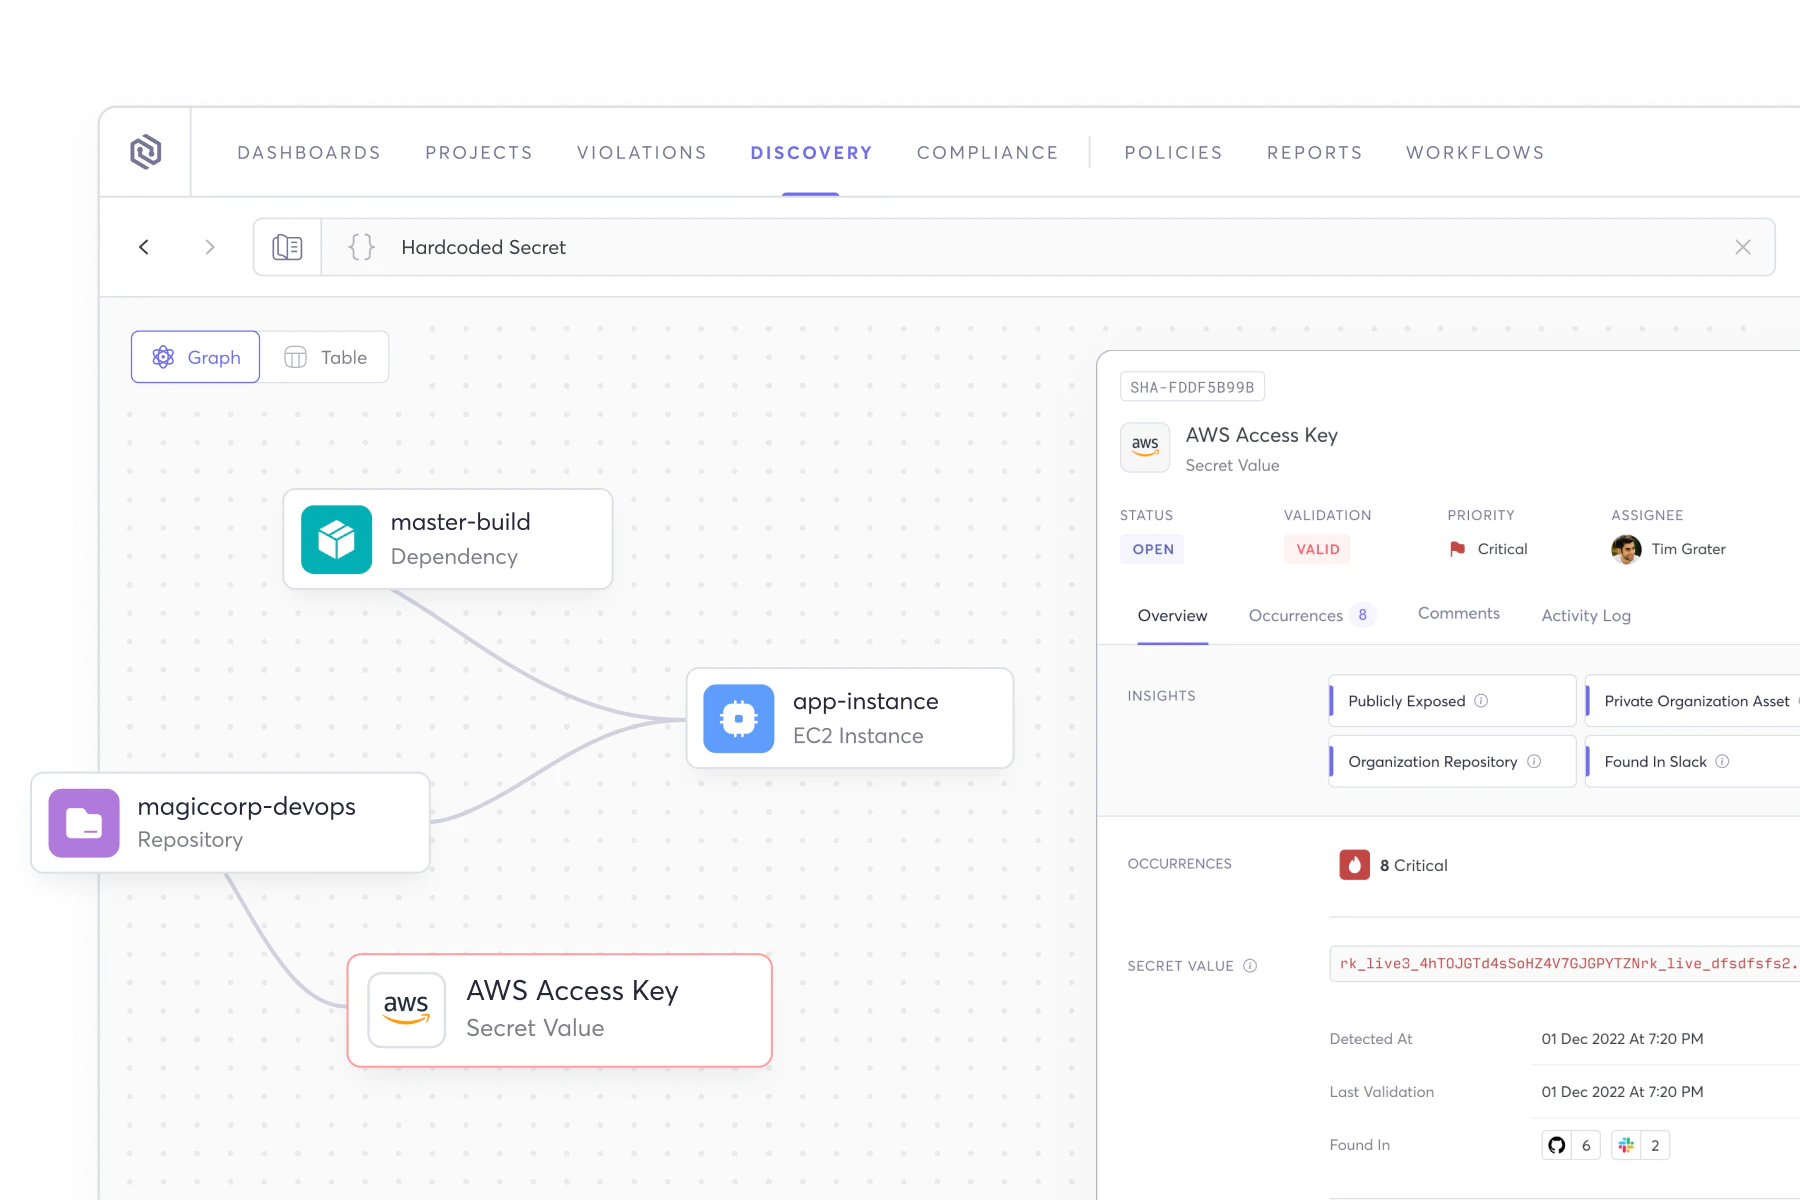
Securing applications and the software supply chain requires understanding the relationships between apps, components, people, tools, pipelines, runtime environments, and risks.
As software development accelerates in the AI era, legacy security tools struggle to keep pace. Cycode offers an Agentic Development Security Platform that delivers faster, more accurate, and developer-friendly security solutions, making Cycode one of the best enterprise Veracode competitors.

Protect Secrets
Identifies secrets across the entire SDLC - source code, build logs, Infrastructure as code, Kubernetes clusters, version histories, Docker images and productivity tools (e.g. Slack).


Detect Leakage
Identifies leakage of private code and secrets in GitHub and GitLab public repositories and code snippets.
Harden SDLC Tools
Enforces secure configurations and best practices.
Secure Code
Identifies vulnerable application code with SAST.
Secure Code Dependencies
Identifies vulnerable code with SCA.
Secure Infrastructure as Code
Identifies IaC misconfigurations.
Protect CI/CD Pipelines
Next-gen SCA to protect against use of insecure tools, modules, dependencies in pipelines, prevent tampering.
Protect Cloud Deployment
Identifies misconfigured cloud resources and drift from IaC.
Scan Fast
Scans source code directly on every commit, with no build or packaging step before results come back.
Reduce False Positives
Delivers high-fidelity findings, with a 2.1% false positive rate on the OWASP Benchmark.
Consolidate Tooling
Unifies AST, supply chain security, and ASPM in one platform, and ingests findings from 100+ third-party tools via ConnectorX.
Protect Secrets
Identifies secrets across the entire SDLC - source code, build logs, Infrastructure as code, Kubernetes clusters, version histories, Docker images and productivity tools (e.g. Slack).
Partial - Limited ability to detect secrets only in code
Detect Leakage
Identifies leakage of private code and secrets in GitHub and GitLab public repositories and code snippets.
None
Harden SDLC Tools
Enforces secure configurations and best practices.
None
Secure Code
Identifies vulnerable application code with SAST.
Secure Code Dependencies
Identifies vulnerable code with SCA.
Secure Infrastructure as Code
Identifies IaC misconfigurations.
Protect CI/CD Pipelines
Next-gen SCA to protect against use of insecure tools, modules, dependencies in pipelines, prevent tampering.
None
Protect Cloud Deployment
Identifies misconfigured cloud resources and drift from IaC.
Partial - Unable to scan in the cloud runtime, can't protect against drift
Scan Fast
Scans source code directly on every commit, with no build or packaging step before results come back.
Partial - Full policy scans run on compiled, uploaded builds, so results arrive after the commit
Reduce False Positives
Delivers high-fidelity findings, with a 2.1% false positive rate on the OWASP Benchmark.
Partial - Higher false positive rates than Cycode in OWASP Benchmark testing
Consolidate Tooling
Unifies AST, supply chain security, and ASPM in one platform, and ingests findings from 100+ third-party tools via ConnectorX.
Partial - AST suite without pipeline security, code leak detection, or third-party finding ingestion

Secure SDLC Foundation
Cycode ensures tools are configured securely, roles are segmented and permissions audited, and security best practices are followed throughout the application lifecycle. This posture layer covers the SCMs, build systems, and registries that Veracode never examines, closing off attack paths that start in tooling rather than in code. Supply chain attacks usually enter through a misconfigured tool, so scanning code alone leaves the front door open.
Pipeline Integrity
Cycode protects code and container dependencies, as well as pipeline dependencies such as open source build tools, pipeline actions and plugins, and infrastructure modules. Cimon, Cycode’s eBPF-based build hardening tool, watches builds as they run and catches tampering in real time. Veracode’s scanners stop at the application layer and leave the pipeline itself unwatched.

Contextual Insights
Cycode monitors the entire SDLC and reports findings with full context so you can avoid manual investigation and prioritize the most important findings. Each finding carries its code-to-runtime trail, including the owner, the exposure path, and whether the vulnerable code is reachable in production. A Veracode report tells you what a scan found, while Cycode tells you which of those findings can hurt you.
Unparalleled Platform
Cycode delivers a seamless user experience with comprehensive reporting dashboards for security pros and deep integrations with developer workflows to shift security left without context switching. Both audiences work from the same data, so the posture a CISO sees in a dashboard matches the prioritized findings a developer sees in a pull request. Nothing needs exporting between tools to keep the two views in sync.
Risk-Based Prioritization
With visibility from code to cloud, Cycode eliminates silos to understand your application, dependencies, CI/CD pipelines, and runtime environments. That context turns a wall of alerts into a ranked queue based on exploitability, exposure, and business impact, cutting developer noise by up to 90%. Veracode scores findings by severity alone, which treats an unreachable flaw the same as one exposed to the internet.
Instant Value
Integrate your DevOps tools in less than one minute to deliver immediate value and allow maximum agility across your SDLC, all without complicated pricing or packaging. First findings arrive the same day the SCM is connected. Veracode onboarding runs application by application, with each one packaged and uploaded before its first scan returns.
Looking for a Live Demo?
Our Cycode experts will answer your questions and provide more info about the platform with a live-action demonstration.
